Millions of cyberattacks through the security hole discovered by AI
Experts assure that frontier artificial intelligence has made cybersecurity problems "more exploitable"
-
CAT -
CAST
BarcelonaThe "backbone of the web" faltered yesterday. The publication of two serious vulnerabilities in PHP, the programming language upon which 70% of the internet's web pages are based, has shaken governments, companies, and users around the world. After administrations in multiple countries decided to halt service on many of their pages while waiting for the update that was supposed to resolve the two problems, attempts to exploit these weaknesses have multiplied. According to the CEO of the cloud services firm Cloudflare, Matthew Prince, the announcement has triggered "millions" of cyberattack attempts exploiting the weaknesses exposed in PHP. "In the 10 hours before it was publicly announced, we saw thousands of attempts to exploit them. They jumped to tens of thousands in the following 45 minutes, and now they are in the millions," Prince explained in a post on his social media page on X.
Two holes of the magnitude of those announced by PHP pose a gigantic impact on the entire network. As detailed by the director of IT and OT security at the technology center Eurecat, Aitor Corchero, the attack vector on this language "does not affect the programming level of a website, but rather would be a direct attack against the engine that executes the code." "And this affects everyone," the expert observes, in conversation with ARA. PHP, it must be remembered, powers around 70% of all web pages in the world. As detailed by the PHP Foundation, the organization that manages this language, the identified holes would allow, under the right conditions, for "an unidentified attacker to execute code" on a server to which they should not have access. The flaws have already been resolved, with updates published by the organization on its website.
According to Wiz, one of the cybersecurity companies that discovered the gap in collaboration with OpenAI, "all versions of PHP from the last decade suffered from at least one of these vulnerabilities." However, the same firm stated that they would have been practically impossible to find without the help of artificial intelligence: "Demonstrating the exploitability of these errors required extremely complex steps, to the limit of what human researchers could achieve." However, the entry of frontier artificial intelligence "has substantially lowered the barrier and made a long-standing error exploitable."
In fact, the foundation itself acknowledges that the problem behind one of the holes identified this week was on the radar of its researchers, who found "the first signs" of this crisis. Although the problem was "theorized," no attack vectors were found that could bring this danger into practice. Corchero attributes this inaction, precisely, to the difficulties in exploiting the problem: "It must be taken into account that many vulnerabilities are found, but the probability of them being exploited is also assessed." The organization, it must be said, has acknowledged that the delay in addressing the problem has been "a structural failure."
AI, a turning point
For Wiz researchers, the affair surrounding PHP is far from being an isolated event. For the firm, in fact, it is a "turning point for the AI era." The crisis, they claim, "illustrates how AI can change the ability to exploit vulnerabilities." In this sense, frontier artificial intelligence models "change how we define which systems are vulnerable in practice." In a similar vein, the CEO of the domain and web hosting provider Cdmon, Jaume Palau, expresses that "AI agents are becoming much better at understanding how code works, and this allows for finding more vulnerabilities of this kind." Regarding this new power, he considers that "risk events will be more common" as the adoption of the technology advances.
In fact, potential attackers are already aware of this paradigm shift, according to what Sergio García, manager of the technology services company i3e, explains to ARA: "Most of the attacks suffered today are carried out with servers that work with AI." Their potential victims, however, do not yet show "mass adoption" of these types of solutions, according to Corchero. Furthermore, defensive products based on artificial intelligence "are under a regulatory framework," while a potential aggressor "does whatever it takes to cause harm."
A threat and a tool
Despite the multiple threats that AI poses to global cybersecurity, the experts consulted choose to see the glass half full. For the executive director of Cdmon, technology and cybersecurity service companies are "the first to use AI, adopt it, and have it ready to improve defense systems." In fact, experts find that episodes like this are, ultimately, beneficial for the stability of the digital world. "There was a weakness that is now resolved, regardless of the incidents that have occurred. Thanks to this, we have better software," states Corchero.
However, Palau urges companies and organizations to use this event to "stay alert." According to the CEO, entities must undertake "continuous risk analysis, safeguards, and investment in good technologies." García shares the optimistic views, and leaves it in the hands of users to take advantage of the defensive potential of AI: "It does not think for itself, it works according to the commands given to it. If we use it to improve our day-to-day life, it will help us a lot."
Effects on companies
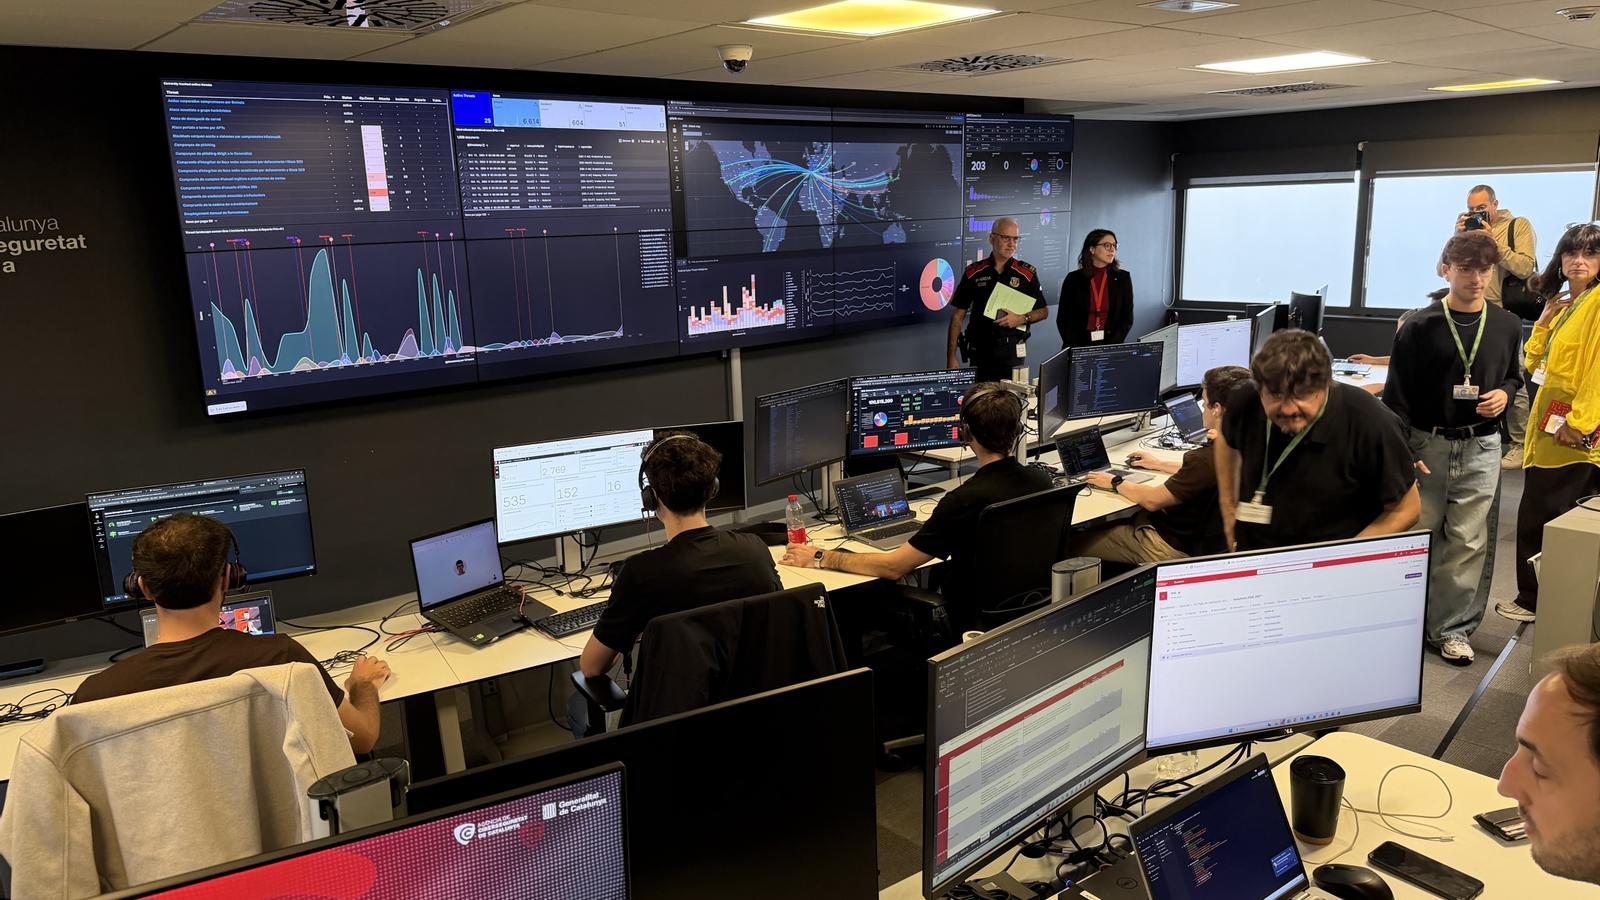
According to Check Point Research, the threat intelligence division of the company Check Point Software Technologies, vulnerabilities in PHP have affected 12% of Spanish companies. The Catalan and Spanish administrations have echoed the digital alerts, through statements from the National Cybersecurity Institute (Incibe) and the Catalan Cybersecurity Agency.
In a publication, the Catalan entity asserts that applying the updates released by the PHP Foundation is "the only measure that completely mitigates the vulnerabilities," although it urges to "monitor the activity of exposed systems and block malicious activity," as well as to inventory all PHP installations to "identify possible vulnerable versions." Finally, it states that it is necessary to check for possible signs of compromise in systems that have been exposed before the update.
